Keep every customer inside their boundary.
We challenge object ownership, tenant controls and hidden role assumptions across the full API.
We test REST, GraphQL and mobile backends as a real attacker would: across roles, tenants, objects and business-critical workflows.
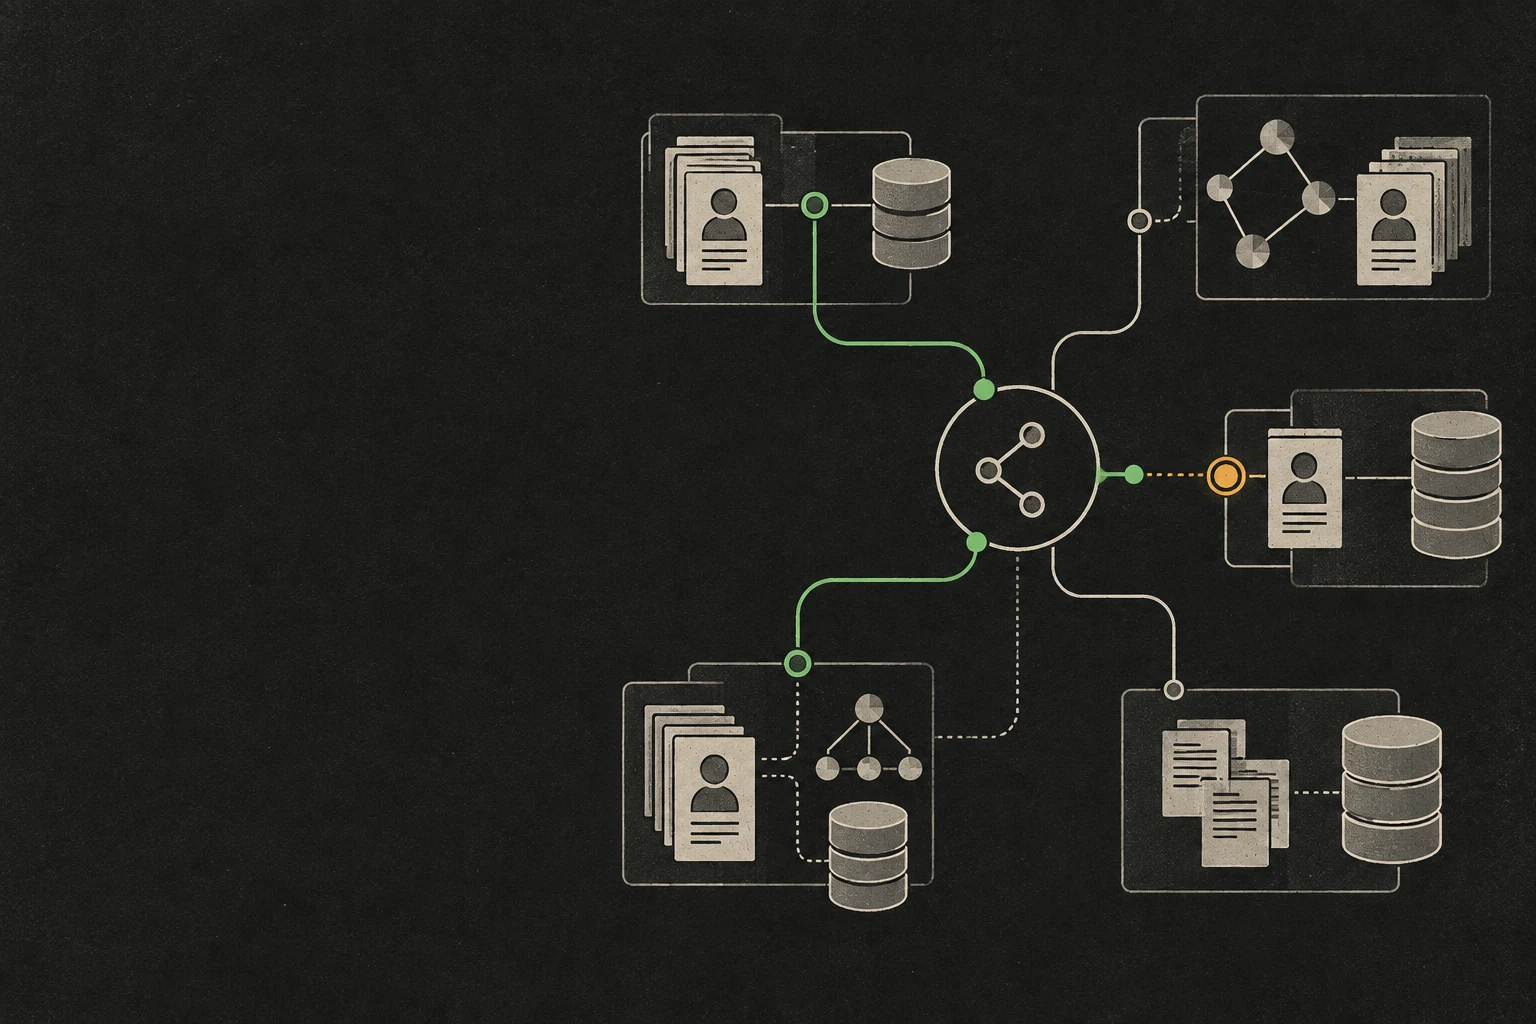
We test the relationships automated scanners cannot understand, then translate every weakness into business impact your team can act on.
We challenge object ownership, tenant controls and hidden role assumptions across the full API.
Abuse testing covers states, sequences and race conditions, not only malformed requests.
Clear evidence and verified fixes support enterprise reviews, partners and internal security decisions.
API risk lives in relationships: who owns an object, which state transitions are valid and what happens when calls are chained.
Object, function and property-level controls across users, roles and organizations.
Tokens, sessions, recovery flows, MFA boundaries and account lifecycle weaknesses.
State manipulation, race conditions, pricing abuse and unintended action sequences.
Excessive responses, hidden fields, enumeration and sensitive data crossing tenant boundaries.
We inventory endpoints, roles, identifiers and the data relationships behind them.
We reconstruct expected permissions and business-state transitions.
We test cross-user, cross-role and cross-tenant abuse, then chain promising weaknesses.
Every reported issue includes concrete impact, evidence and a retest after remediation.
Each issue connects the affected request to the broken security assumption and the business impact.
Endpoint and role coverage
Request-level reproduction steps
Authorization matrix gaps
Attack-chain evidence
Risk-based prioritization
Remediation verification
Multi-tenant SaaS platforms
Fintech and transactional APIs
Mobile application backends
Partner and public API programs
Tell us about the API surface, authentication model and roles. We’ll help define a focused assessment.
contact@olivex.io